

Build for the Future: Make Foundational AI Work for You
Foundational AI pays off fastest when you point it at the tedious work your engineers dread. A well-scoped model can spot unusual patterns in seconds and suggest what to do next, saving analysts hours each week. That’s where foundational AI delivers immediate enterprise value.
Artificial intelligence (AI)covers a lot of ground, from the machine learning models behind fraud detection to the large language models behind today’s chatbots and AI agents. Foundational AI — a large, pre-trained model your team adapts to a specific job — sits in the middle of that shift. But plugging these AI systems into your network without a plan creates real security risk: more data moving through more places, and more chances for something to go wrong.
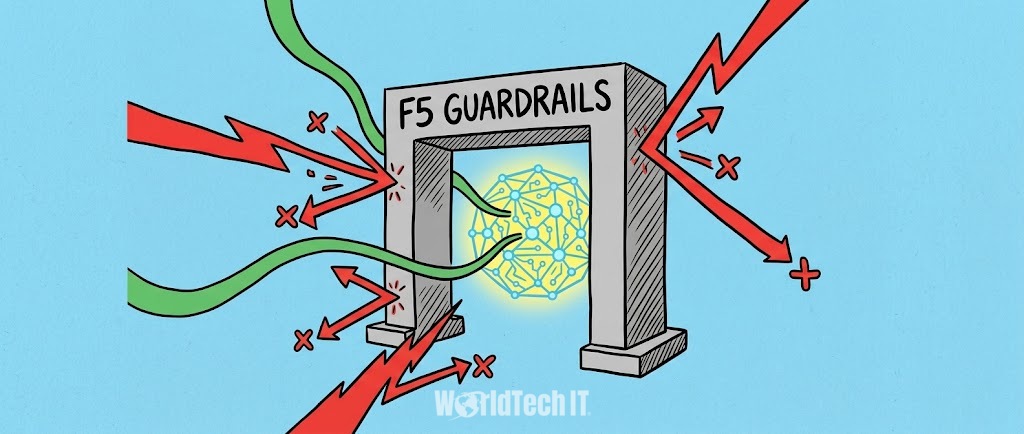
The trick is not hiding from the technology out of fear of hallucinations or compliance gaps. An AI gateway like F5’s AI Guardrails enforces clean operational guardrails.
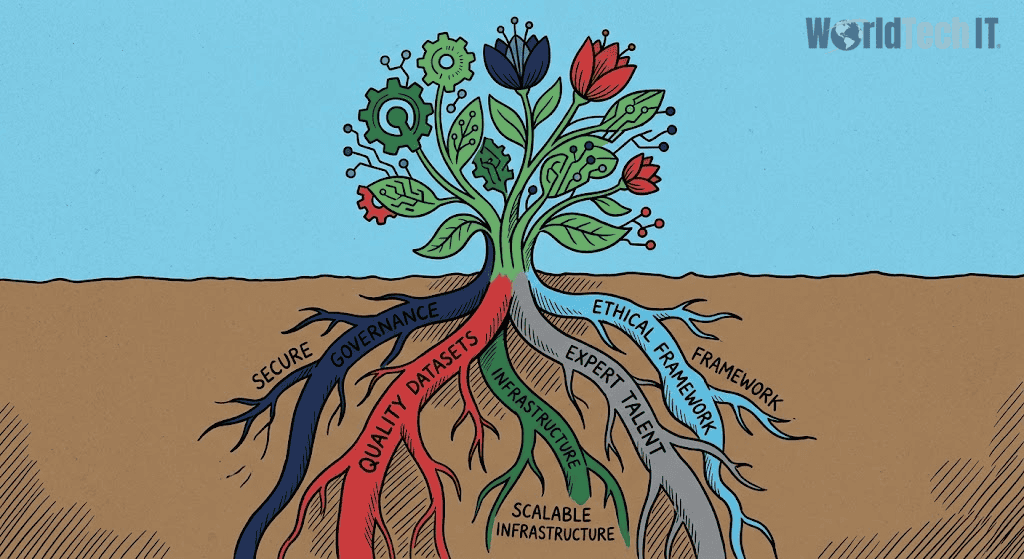
WorldTech IT helps you get past early deployment issues and build a stable environment with scalable F5 Distributed Cloud multi-cloud networking. Together with F5, we set up the network so you can use foundation models safely and at scale for enterprise AI. The rest of this post walks through how that streamlining actually happens, and where it earns its keep.
What Are F5’s AI Guardrails?
In short, it is a control point that helps protect what goes in and out of your large language models. It manages access, usage, and prompt security in one place. IBM’s explainer on what an AI gateway is frames it well: think of it as a reverse proxy purpose-built for AI. Modern AI gateways give enterprise security teams one place to enforce security rules before models access sensitive systems.
In short, it helps protect what goes in and out of your large language models. It manages access, usage, and prompt security in one place. IBM describes an AI gateway as a reverse proxy built for AI. Modern AI gateways give enterprise security teams one place to enforce security rules before models access sensitive systems.
It also lets your compliance team apply the same security standards to AI as they do to other applications.
What Are the Root Advantages: Why does it matter for your Foundational AI?
AI’s upside is broad, but breadth alone doesn’t build a business case. Here is where enterprise teams see the clearest return.
- Threat spotting: A model can review logs, spot unusual patterns, and suggest next steps. Done right, this is a foundational AI model that secures you, not against you.
- Speed and scale: Every LLM, regardless of type, shares one appeal. It automates routine work so your team can focus on the triage that genuinely needs a human. That’s real AI assist, and it’s why more teams are turning to enterprise AI solutions.
- Traffic smoothing and pre-allocation: A model can predict traffic spikes and add more resources before demand increases. Spikes are unpredictable, but with the right AI infrastructure in place, autoscaling serves as a buffer that prevents bottlenecks.
- Model agility and abstraction: Describe what you need in plain English instead of writing complex commands. Roll out changes in small steps, and when something breaks, spot it and roll back.
The Attack Surface Foundational AI Creates
Ever stop to think about what happens the second you plug a brand new model into your network? Whether it’s a chatbot that reads internal docs or an agent that takes action, it creates a new path into your network. That expands your attack surface, just like a new API or remote-access tool.
Here’s the thing though — most security teams haven’t had to watch for this particular flavor of trouble before. AI brings its own security vulnerabilities: prompt injection, data theft through carefully worded questions, and models that reveal more data than they should.
Attackers are already using AI-powered tools to find these weak spots at scale. That part keeps me up at night a little, honestly.
Now, I’m not saying any of this to scare you off foundational AI. Far from it. I’m saying it because you test everything else exposed to the internet, so why would AI get a pass?
Add your AI endpoints to your existing penetration testing program for web apps and APIs. Use the findings to improve your guardrails instead of guessing.
Fair warning: expect some false positives at first. That’s part of tuning the system to your environment. Annoying? Sure. But it’s cheaper than dealing with an incident.
The takeaway: integrate security into the AI pipeline from the start, not after the model ships. F5 AI Guardrails do exactly that.
Security at the Edge: Added Runtime Layer for your Foundational AI
The case for edge inspection is straightforward. Traditional API and application security tools were built for deterministic traffic, and AI traffic is anything but. As F5 argues in its AI Gateway announcement, existing API and app security is not enough on its own. Inspection has to move up to the AI layer, pre-qualifying prompts and responses before they reach the model or your core systems.
For more insights on securing AI at the edge, follow WorldTech IT on LinkedIn.
High-Impact Enterprise Use Cases
Want your model to know your business, not just the internet? That’s what secure knowledge tools do. They use private data like SharePoint and PDFs from your enterprise network instead of guessing, while keeping that data off the public internet.
And don’t forget Access control. It should follow your existing permissions, so Bob in accounting still can’t see engineering docs just because he asked the chatbot nicely. Here is more possible use cases:
- Automated middleware: Connects systems that don’t naturally work together. You can describe the connection in plain language and make changes in minutes instead of spending a whole sprint on them.
- RAG: Finds the right documents first, so the model gives more current answers with fewer hallucinations. Point it to a live data source like your internal wiki.
- Caching: Remembers common questions so the model doesn’t have to answer them from scratch. This can make responses much faster.
Guardrails for AI Agents
AI agents raise the stakes: they don’t just give answers. They take action, like booking meetings, opening tickets, or moving files, often without human approval.
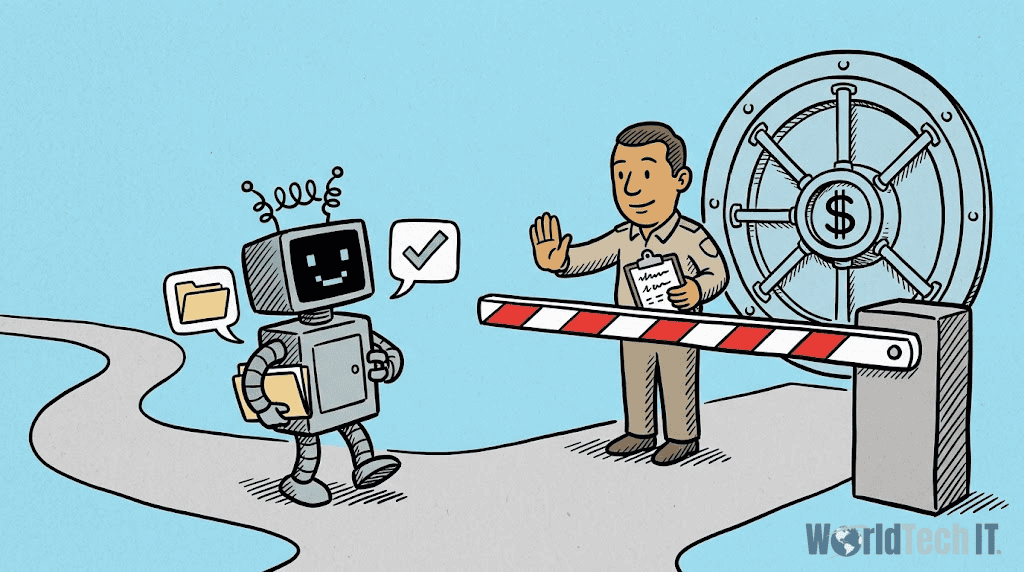
The more an agent can act on its own, the stronger your guardrails need to be. Think of an agent like a contractor with your credit card and keys. Set clear limits upfront. Start with permissions.
Limit what the agent can access, including your CRM, ticketing system, and payment processor. If it shouldn’t transfer $50K, change access, or email the CEO, it shouldn’t have access to those systems.
Then audit every action. Track every ticket, file, and email so you can see exactly what happened if something goes wrong. Finally, build in a pause. If an agent tries something unusual, like a large transfer or permission change, stop it and ask a human to approve it. Not every action needs approval, but the big ones do.
None of this is a reason to avoid agentic AI. It’s a reason to build the oversight in from the start, before the first agent goes into production.
Architecting the Future: The WTIT and F5 Advantage
The end state is a private, secure enterprise AI platform your teams can actually trust in production.
For F5 AI Gateway deployments, we deploy F5 AI Guardrails as an intelligent reverse proxy in front of your models, giving you centralized visibility, semantic caching, and content-based routing from a single control point instead of bolting policy onto each application.
On the WTIT engineering side, our professional services team designs, scales, and maintains the private, high-performance LLM infrastructure underneath, from compute and networking to the guardrails that keep it compliant as you grow.
Combined with F5’s AI-discovery platform, acquired through SurePath AI, F5’s AI Guardrails also give you a way to contain AI workloads internally without worrying about the risks of shadow AI running unmonitored.
Conclusion & Next Steps
The real work is in the pipeline, not the model. Getting value from foundational AI is less about the model and more about the network and guardrails around it. Nail that, and the model becomes something you can put into production without holding your breath.
If you’re evaluating AI solutions for a regulated environment or already have foundational AI running without guardrails, we’d like to help. Talk to the WorldTech IT engineering team for an infrastructure review. We’ll help map out a secure, scalable setup for your environment.


Leave a Reply